Kingskawn
Established Members
-
Joined
-
Last visited
-
Seems that it's normal it won't work while we have a remote Wsus (SUP) server. So when it's hosted onto the same site server (primary) it will work but when you have a dedicated wsus it won't ?
-
We are have this error too Kirill_L but we install bitlocker through Intune, not from SCCM, the machines are co-managed. But for some weird thing 2% of our machines don't receive the encryption policy so 300 machines are still without encryption. The others went well
-
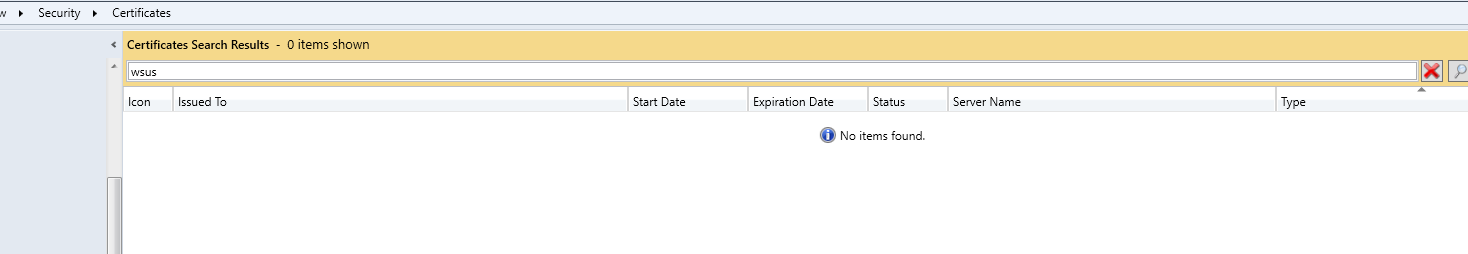
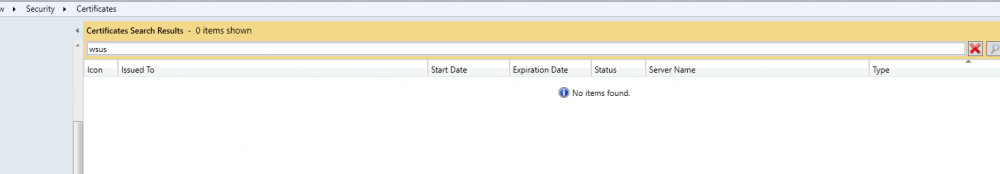
Nothing in there ? I configured it with extended HTTPS. In my lab I have the same configuration and it works. A while ago I configured third party updates in prod and the certificate was created by the server but I had to delete the setup and it doesn't create the certificate now.

-
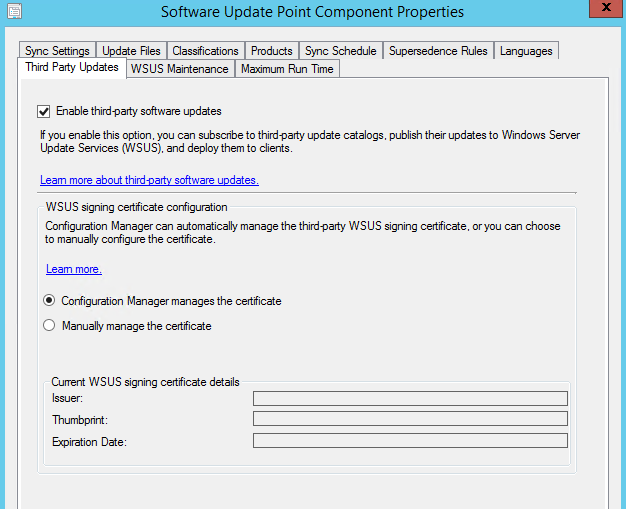
I configured the 'third party updates' option but it seems there's no certificate that gets created. I already unchecked the option and resync the windows updates and after this re-enabled the option but it keeps empty. Anyone?
-
It's ok, triggered a heartbeat onto the collection and the info was updated
-
I have some servers being seen as physical machines 'Virtual Machine = no' while these are virtual machines running ESX. I can create queries for collections but on what is the value based in the console?
-
I have the msedge_installer.log but there's no reference to azure or web page content ? msedge_installer.log
-
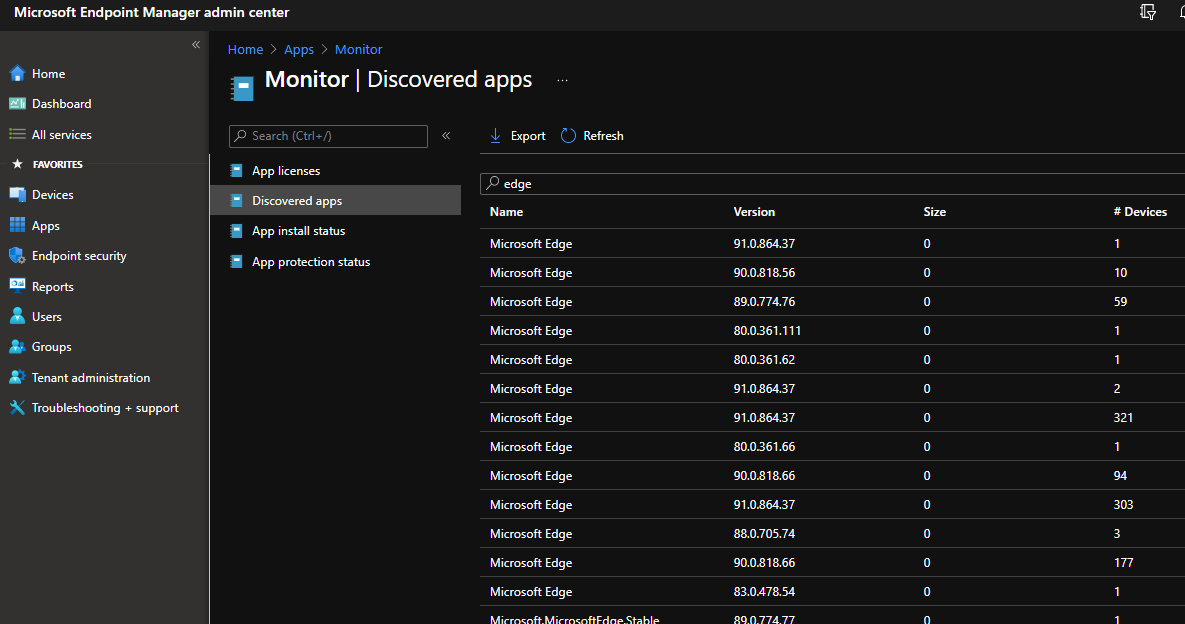
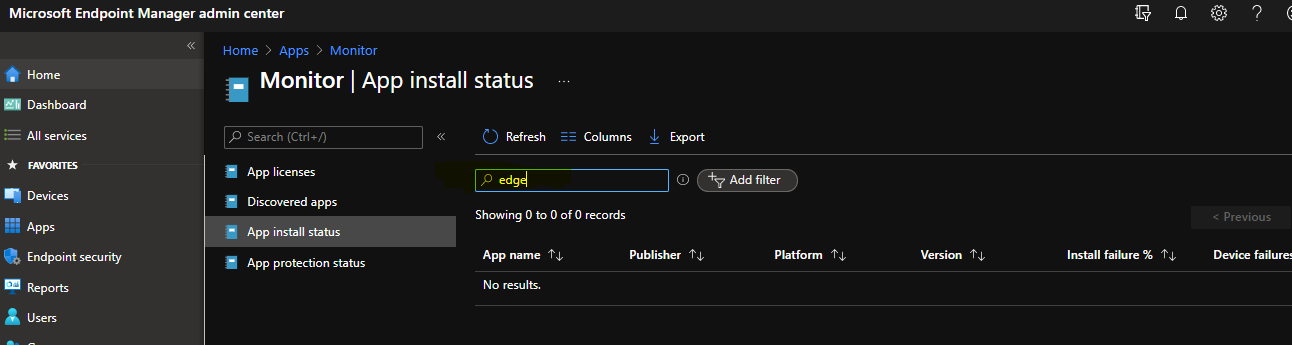
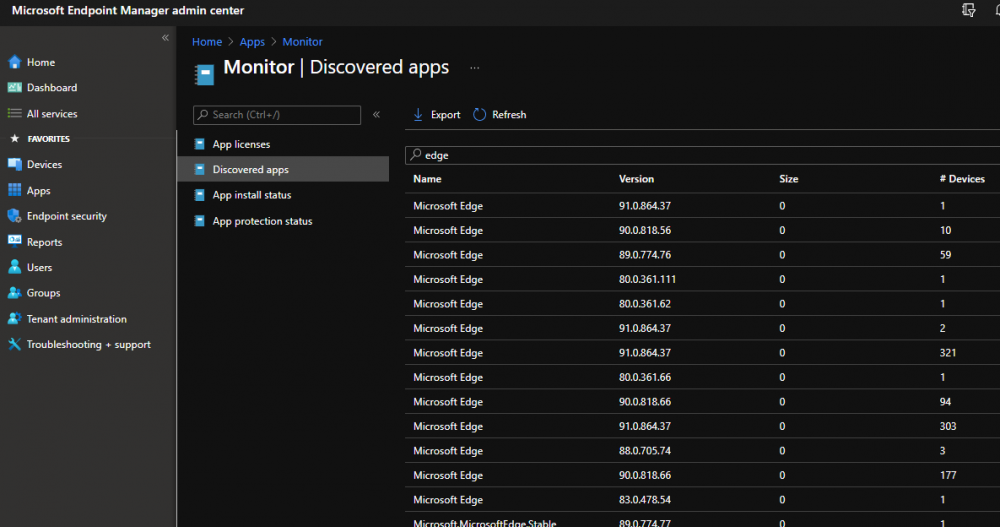
Niall, I don't see any app status 'Edge' in Endpoint Manager admin center. What I can see is the Discovered apps and versions These are the workloads for now with co-management
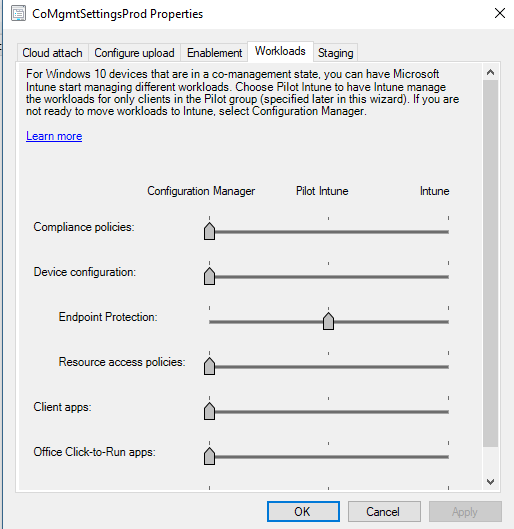
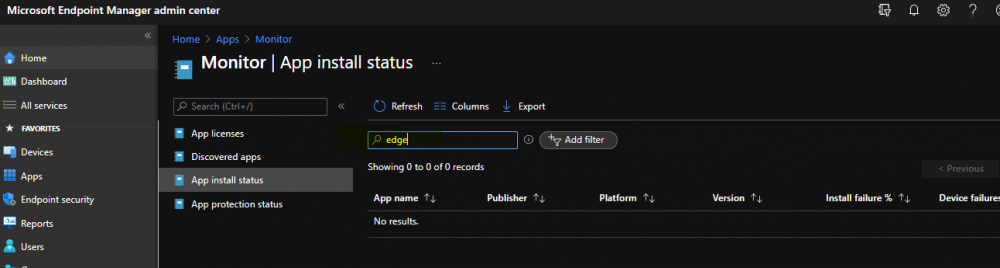
-
Yes it is
-
Edge is updating itself while we are using SCCM to manage the updates as this printscreen is proving When I go to the CM console you can clearly see this update isn't deployed nor downloaded to the package. It isn't even advertised on The latest deployed version is 90.0.818.66 In Intune we don't have an application to install so I cannot figure out, for now, where this thing is coming? Any ideas?
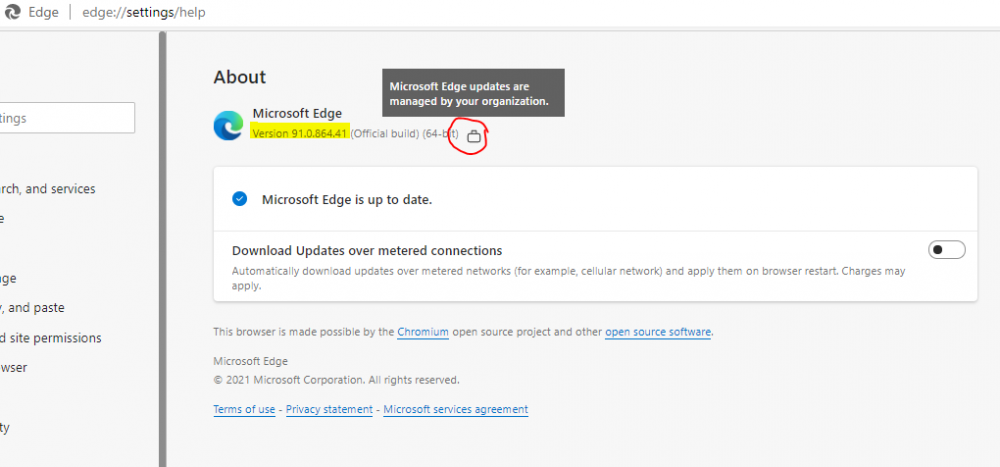


-
Ok, it worked to have the WinRE but when I looked to Azure the bitlocker key was vanished so now I don't know to get the data back. I hope he saved his stuff to OneDrive before
-
Yes, I have the recovery key from Azure. I'll try the 3 times step and hopefully the recovery will launch.
-
I have a machine which gives the error 8007139f when starting the machine. The bitlocker recovery is running but 1sec later the BSOD comes up. There is still some data on the machine which I need to access. Maybe I can take the disk out and access with an external usb cable/dock? What solutions are there?
-
Hi Garth, I tried the trick with ospp.vbs as I used to on Office 2010, 2013 and 2016 but as our licenses are activated from the cloud it's like not working. This is the output I get: To find them we can check on the existence of the folder and tokens created in -> \AppData\Local\Microsoft\Office\16.0\Licensing But this is per user.
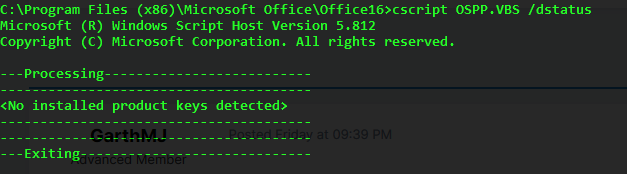
-
Some end-users are having some trouble with 365 Apps (O365ProPlusRetail) that says there license is not valid or active. I want to make a query or something to group these machines and apply a regfix. But for that I need to find them. We had the ospp.vbs /dstatus before but as the license comes from the cloud (not mak nor kms) I don't know how I can see this. There is a nice guide of Eswar Koneti but not doable for us : https://eskonr.com/2019/09/check-microsoft-office-activation-status-using-sccm-compliance-settings/