soultrain99
Established Members
-
Joined
-
Last visited
Everything posted by soultrain99
-
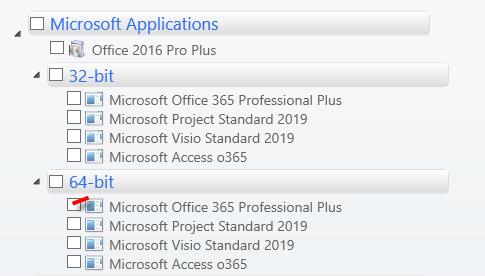
In my screenshot below. When setting up applications and packages in the UDI Wizard, for example: If the 64 bit version of Office 365 is selected, how can i prevent the Office 2016 and all the 32-bit versions from being selected?
-
soultrain99 replied to soultrain99's topic in Deploying Windows 10, Windows 8.1, Windows 7 and more...So correction. Putting ConfigMgr Remote Control Users into the local computer seemed to fix the problem. I added this as command line to my TS: cmd /c net localgroup "ConfigMgr Remote Control Users" /add
-
soultrain99 replied to soultrain99's topic in Deploying Windows 10, Windows 8.1, Windows 7 and more...someone also mentioned to put ConfigMgr Remote Control Users with no members. https://social.technet.microsoft.com/Forums/windows/en-US/4170fdd4-462d-41b4-9cd9-14466ec70cda/timed-out-waiting-for-ccmexec-service-to-be-fully-operational-failed-to-wait-for-ccmexec-service-to?forum=configmgrgeneralStill didnt work.
-
I have done windows 7 to windows 10 upgrade version 1607 with no issues. It does the upgrade in about 1 hour. Which is great. With 1703 it takes about 2.5 hours. It sits on Waiting for service CcmExec to exit pending state 3 for over 1 hour. I think that CCMEXEC.exe is trying to start but its in a stopping state. I remoted into the services on the I read somewhere that there's a service that was dependant on it and that dependency can be removed by putting this in the beginning of the TS: sc config "smstsmgr" depend= "" Still doesnt work. Not sure if anyone else ran into this. Executing C:\WINDOWS\ccmsetup\ccmsetup.exe /remediate:client /OSUpgradeRepair OSDUpgradeWindows 2/22/2018 5:58:57 PM 4972 (0x136C) Command line for extension .exe is "%1" %* OSDUpgradeWindows 2/22/2018 5:58:57 PM 4972 (0x136C) Set command line: "C:\WINDOWS\ccmsetup\ccmsetup.exe" /remediate:client /OSUpgradeRepair OSDUpgradeWindows 2/22/2018 5:58:57 PM 4972 (0x136C) Executing command line: "C:\WINDOWS\ccmsetup\ccmsetup.exe" /remediate:client /OSUpgradeRepair OSDUpgradeWindows 2/22/2018 5:58:57 PM 4972 (0x136C) Process completed with exit code 0 OSDUpgradeWindows 2/22/2018 6:21:10 PM 4972 (0x136C) CcmSetup remediate succeeded. OSDUpgradeWindows 2/22/2018 6:21:10 PM 4972 (0x136C) SMS Client remediated OSDUpgradeWindows 2/22/2018 6:21:10 PM 4972 (0x136C) Enabling CCMExec service OSDUpgradeWindows 2/22/2018 6:21:10 PM 4972 (0x136C) CcmExec service startup type is set to automatic OSDUpgradeWindows 2/22/2018 6:21:10 PM 4972 (0x136C) Taking the client out of provisioning mode OSDUpgradeWindows 2/22/2018 6:21:20 PM 4972 (0x136C) getPointer()->ExecMethod( BString(pszObject), BString(pszMethod), 0, 0, pInParams, ppOutParams, 0 ), HRESULT=80004005 (..\WmiNamespace.cpp,1391) OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) ns.ExecMethod( c_szWmiClass_SmsClient, c_szSetProvisioningMode, inParams, &outParams ), HRESULT=80004005 (..\ProvisioningMode.cpp,64) OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Could not execute WMI method SMS_Client.SetClientProvisioningMode OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Exiting SetClientProvisioningMode 0x80004005 OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Starting CCMExec service OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Waiting for service CcmExec to exit pending state 3 OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Waiting for service CcmExec to exit pending state 3 OSDUpgradeWindows 2/22/2018 6:26:29 PM 4972 (0x136C) Waiting for service CcmExec to exit pending state 3 OSDUpgradeWindows 2/22/2018 6:26:30 PM 4972 (0x136C) Waiting for service CcmExec to exit pending state 3 OSDUpgradeWindows 2/22/2018 6:26:30 PM 4972 (0x136C) Waiting for service CcmExec to exit pending state 3 OSDUpgradeWindows 2/22/2018 6:26:31 PM 4972 (0x136C)
-
I used SCCm to upgrade from 7 to 10 and received the same error. I upgraded my .NET to 4.7 on the client machine and Software Center started working for me.
-
So if the machine is removed from AD a year ago, will MBAM still keep the Recovery Key in its DB? If i needed to unlock the HD?
-
Setting: I have an MBAM server 2.5. sp1 which is integrated with SCCM 2012 r2. The Recovery Keys are in its DB as well as AD. Scenario: I took a hard drive out of a machine (WS1) and placed into a USB HD enclosure which i attached to another machine (WS2).`The drive came up saying it's encrypted and if i try to unlock it, It asked for the Recovery PW. I noticed that when i used the the self-service page to recover a the password it said "invalid Key" I looked at the SQL and ran this query: SELECT TOP 1000 [Id] ,[LastUpdateTime] ,[VolumeId] ,[RecoveryKeyId] ,[RecoveryKey] ,[RecoveryKeyPackage] ,[Disclosed] FROM [MBAM Recovery and Hardware].[RecoveryAndHardwareCore].[Keys] I saw the Recovery ID key in SQL and tried it via AD and it gave me the same password. When i opened the AD object and looked under the bitlocker Tab i saw all the recovery IDs there was one that was never made it to MBAM DB. I used that one and it unlocked. I have 2 questions: 1) How can it populate the MBAM DB simultaneously as AD? 2) Lets say that I had removed the (WS1) computer 1 year ago and needed to recover the data. Where would i find the key? I just want to make the recovery process as painless as possible for the Helpdesk.
-
I upgraded SCCM 2012 r2 to SP1. I went to add drivers to an existing boot image and noticed the boot images version 6.3.9600.x are not showing up. I created a new boot image and it shows up in the list. I have ADK 8.1 and 10 installed before the upgrade. We still deploy Windows 7. So the question is if I create a new Boot Image version 10.x can it be used to deploy Windows 7?