




Nemanja Jovic
Established Members
-
Joined
-
Last visited
-
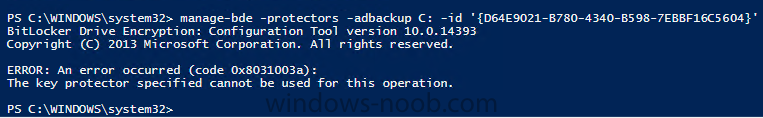
Hello everyone, I have the client that wants to do something specific with bitlocker and its pins, but that is beyond of this topic. Issues is: When you create a step in task sequence to set up the bitlocker, if you choose TPM and PIN, you will be able to backup the recovery key into Active Directory. But, if you try to do the same via command line on the client, you will get the error: The key protector specified cannot be used for this operation. Somebody have a clue how to overcome this, since we really want only to use TPM and PIN and to store recovery key in AD, for specific reasons, we have to use command line to setup the Bitlocker. Thanks,
-
Basically we have one Primary site and few distribution points on branch sites. Our current version of SCCM is 2012 R2 1710. We do not want to upgrade it to version 2016, we would like to install a new fresh server with SCCM 2016 on it. Question is, is it possible to transfer all of the roles and put it as a primary, after that to decommission the 2012 ? Thanks in advance!:)
-
Hello, Seems like MS article that explains usage of Invoke-CMReport is a bit missleading. In order to call report, try syntax like this: Invoke-CMReport -ReportPath "Endpoint Protection/Computer Malware Details" -ReportParameter @{ Collection = “MyCollection”; “Time Range” = “4 weeks” } I hope this is informative for you, cheers.
-
Great walkover, we really appreciate sharing this kind of quality on one place, I would just add publishing SPN to this post, everything else is magnificent. Cheers!
