




SCCMentor
Established Members
-
Joined
-
Last visited
-
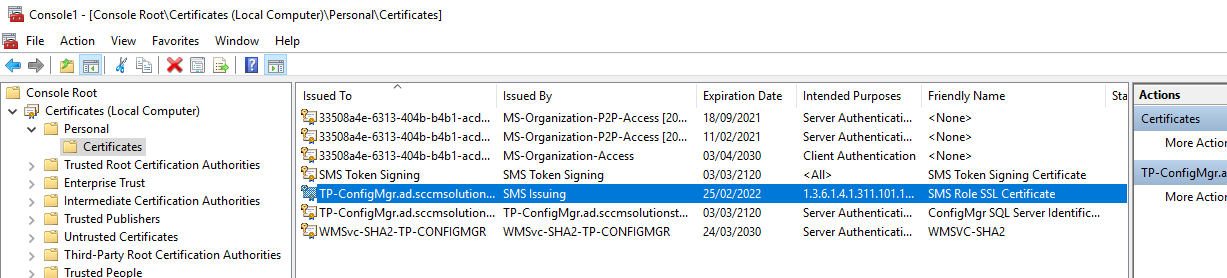
I tested this. I unchecked the box to remove eHTTP. I deleted the SMS Role SSL Certificate certificate from local machine. I wasn't able to select Not Selected - greyed out like you said. I then re-enabled eHTTP, it recreated the SMS Role SSL Certificate and I then set this in IIS.
-
Yes that's the cert. Was it generated by Configmgr or did you copy it from the other box?
-
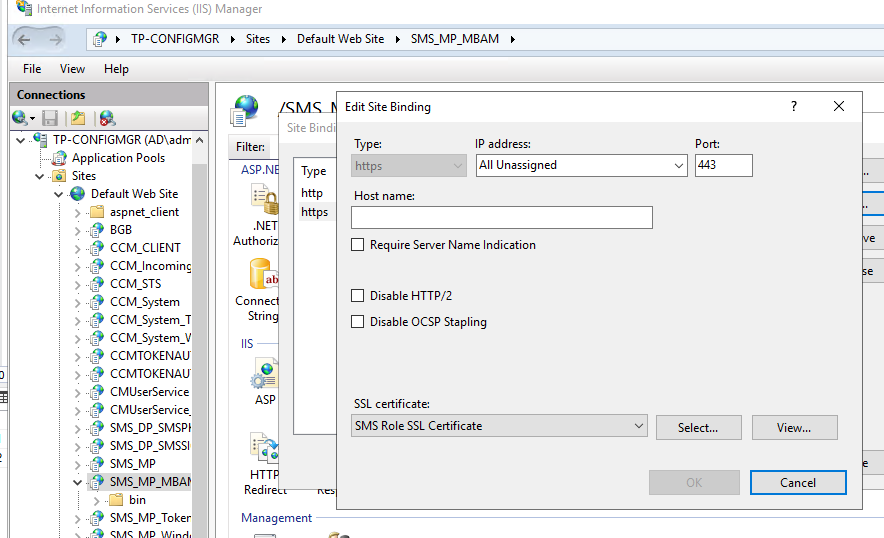
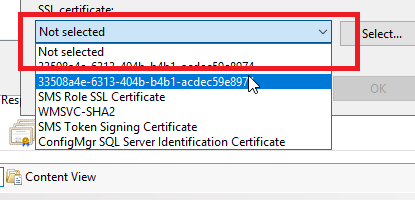
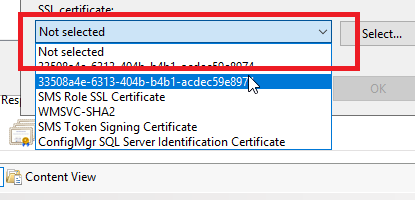
From the list of certs in the IIS bindingOK this will be potentially the problem then. So remove eHTTP by unchecking the box. Set the IIS SSL cert to 'Not selected' Keep an eye on the sitecomp and mpcontrol logs and ensure they complete removing eHTTP - just watch them until they stop churning over. Reenable the check box. Watch the sitecomp log again, keep an eye out for 'Detected change in SSLState for client settings' Then check back in certlm.msc for the SMS Role SSL Certificate cert in the personal store and then see if it's bound to IIS. At that point, restart the ccmexec services on the endpoint and see what clientidmanagerstartup log does. Does it get an 'Retrieved Certificate options successfully' entry and then check for cert?
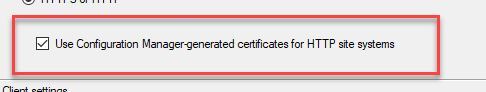 Do you have a cert called SMS Role SSL Certificate? This is generated by when enabling eHTTP and is automatically bound to IIS. If you were running full PKI previously it's possible that hasn't been set (I've seen this happen before where the SMS Role SSL Cert doesn't get generated due to an old PKI cert) Check for the cert in your certlm.msc console on the server running the MP Note also that the errors you have in the clientidmanagerstartup and cert maintenance logs - I get these also in my eHTTP site. I've noticed that the ConfigMgr applet doesn't have all the tabs and that the clientidmanager log still reports are registration pending. Does the client complete registration? Hard to know when we are working off screenshots. Cheers
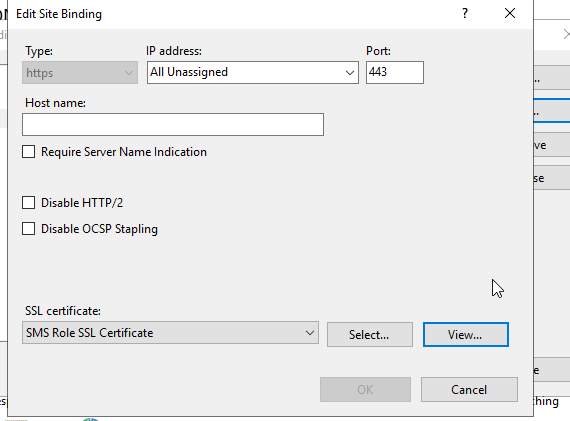
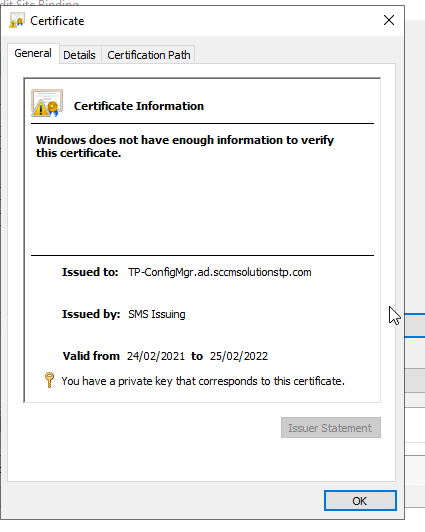
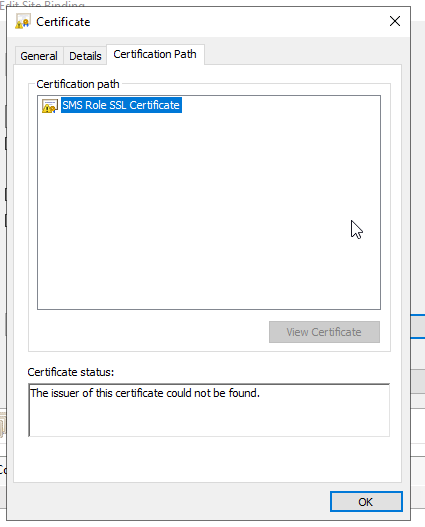
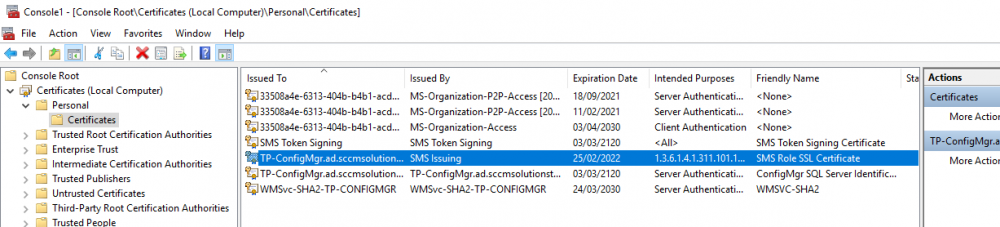 What cert is bound to IIS?The eHTTP MP should be sufficient for this to work. Has the SMS Role SSL Cert automatically bound to the IIS or been changed at all? Are you able to share the BitLockerManagementHandler log at all? Cheers Paul
 No. Since the process will need to talk to the MBAM endpointsThis shows you how to add a .exe to ConfigMgr https://sccmentor.com/2013/06/12/deploying-exe-files-via-sccm-2012/Run a WMIC query on the machine to get the details CSProduct Get Name https://sccmentor.com/2013/05/20/find-out-the-computers-model-type-from-a-wmi-query/you can mount the wim and inject the cab files. https://sccmentor.com/2013/06/11/add-language-packs-to-an-offline-wim-file/BTW MS released a support matrix for Windows 10 ADK. It is not supported on 2012 https://blogs.technet.microsoft.com/enterprisemobility/2016/09/09/configuration-manager-and-the-windows-adk-for-windows-10-version-1607/Feel free to post any comments on my blog as well. I'd like to collate any notes from the field to assist people when running this in PROD environments. Cheers Paul

Important Information
We have placed cookies on your device to help make this website better. You can adjust your cookie settings, otherwise we'll assume you're okay to continue.